TheJavaSea.me Leaks AIO-TLP371: Risks, Safety, and What Is Verified
Have you ever seen a strange file name trend overnight? That is what happened with TheJavaSea.me leaks AIO-TLP371.
Posts, search suggestions, and blog articles now repeat the phrase. Yet solid proof is hard to find. As of October 2026, this guide sorts fact from rumor so you can protect yourself.
What Is TheJavaSea.me Leaks AIO-TLP371?
The phrase TheJavaSea.me leaks AIO-TLP371 joins a website name with a file label. Online posts link it to an alleged data leak or a bundle of shared files. So what is TheJavaSea.me leaks AIO-TLP371, in plain words? It is a search term tied to a TheJavaSea.me leak archive that nobody has proven. No trusted public source lists what sits inside. The AIO-TLP371 file may be real, edited, or even empty.
Popularity does not equal proof. Many sites repeat the same claim, and that makes it look strong. However, repeating a rumor ten times does not make it true. Good leaked information verification asks one simple thing. Where did the claim start? Until a clear answer appears, treat every detail as a rumor.
A loud rumor is still a rumor. Volume is not evidence.
What Is Known About TheJavaSea.me and AIO-TLP371?
Very little is solid. Many pages mention TheJavaSea.me AIO-TLP371, yet few cite a primary source. No affected company has come forward. No regulator has posted a notice. No known security researcher has published a report. Because of this, the AIO-TLP371 verified information list is short. Most of what you read is guesswork wrapped in confident language.
Experts call the next problem an “information echo.” One site posts a claim. A second site rewrites it. A third site cites the second. Soon dozens of pages seem to agree. Yet they all trace back to one weak source. This pattern fuels cybersecurity misinformation and makes data leak claims feel stronger than they are.
What Does AIO-TLP371 Mean?
The AIO-TLP371 meaning is not documented anywhere official. “AIO” usually stands for All-In-One, so many readers treat it as an All-In-One file collection. “TLP371” looks like a release or package tag. It is one of many unknown file identifiers that circulate online. The number 371 may be a version, a batch, or a random tag. Nothing proves it counts victims or file size. Anyone who gives an exact meaning is guessing.
Does TLP371 Refer to the Traffic Light Protocol?
No, it does not. The real Traffic Light Protocol TLP 2.0 comes from FIRST, the Forum of Incident Response and Security Teams. It tells people how far they may share sensitive information. These FIRST cybersecurity standards include five official TLP classifications. TLP:CLEAR replaced the older TLP:WHITE label in version 2.0. TLP371 is not on the list. FIRST says only its own labels count as valid TLP labels.
| Official TLP 2.0 Label | Sharing Rule |
| TLP:RED | Named recipients only |
| TLP:AMBER+STRICT | Recipient’s own organization only |
| TLP:AMBER | Recipient’s organization and clients who need it |
| TLP:GREEN | Wider community but not public |
| TLP:CLEAR | No limit on sharing |
Is AIO-TLP371 a Confirmed Data Breach?
Not at this time. So is AIO-TLP371 a confirmed data breach? The honest answer is no. A real breach usually leaves a paper trail. You might see a company statement, a regulator filing, a researcher report, or an entry in a trusted breach database. None of these exist for this label. A lack of proof does not mean the files are fake. It only means no one can say what they are. A careful data breach investigation needs facts before it needs headlines.
What Information About AIO-TLP371 Remains Unverified?
Almost everything beyond the name. The AIO-TLP371 unknown contents include the file types, the source, the age, and the owner of the data. Nobody has shown a record count or a victim list. Nobody has shown how the data was taken. Claims about passwords or bank details are also unconfirmed. Treat each of these as a blank until a trusted researcher fills it in. That is the heart of breach verification.
Why Is TheJavaSea.me Leaks AIO-TLP371 Trending?
Odd names grab attention fast. A label like AIO-TLP371 sounds technical and secret. It looks like something insiders know. That feeling pushes people to click. Search engines then notice the clicks and show the phrase to more people. The loop feeds itself. This is how a small rumor becomes a trend with almost no new facts.
Content sites also join in. They see rising searches and publish quick posts to catch the traffic. Many copy each other. A few add made-up details to sound complete. As a result, data leak claims spread faster than any check can follow. Good cyber threat awareness means pausing before you believe a trending term.
Curiosity About Unfamiliar File Names
Think of finding an unmarked box in the attic. You want to peek inside. An unfamiliar file name works the same way. It stirs curiosity, and curiosity lowers your guard. Scammers know this trick well. They use unknown file identifiers as bait because the mystery does the selling for them. Before you click, ask one question. Would I open this box if a stranger had left it on my doorstep?
Online Discussions, Forums, and Search Suggestions
Forums and chat groups add fuel. Someone asks what the label means. Someone else guesses. A third person repeats the guess as fact. Meanwhile, search autocomplete shows the phrase to new users. Each new search makes the term look more important. This cycle can run for weeks without any real evidence. It shows why online information credibility matters more than search volume.
Interest in Bundled Files and Alleged Data Leaks
Bundles attract attention because they promise a lot in one place. An All-In-One file collection sounds like a treasure chest. Yet bundles often hold old material. In 2019, a huge pile called “Collection #1” made headlines. According to Have I Been Pwned, it mostly merged recycled leaked databases and held hundreds of millions of email addresses. Much of it was already public. This case shows why a new name does not always mean a new attack.
Is TheJavaSea.me Safe or Legit?
Be careful. Little public information exists about who runs the TheJavaSea.me website. Without clear owners, policies, or contact details, you cannot judge trust. A proper TheJavaSea.me security analysis would need technical testing that most readers cannot do. So the safest view of TheJavaSea.me safety and legitimacy is simple. Assume risk until proven otherwise.
You also cannot judge safety by looks. A clean design means nothing. Scam pages copy trusted brands every day. They add logos, badges, and fake reviews in minutes. Therefore, rely on checks and not on feelings. Visiting suspicious download websites can expose you to online security threats even if you never click “download.”
Warning Signs of an Untrustworthy Website
Learn the red flags. Good suspicious website verification starts with what you see on the page. The table below shows common suspicious website warning signs and why each one matters.
| Warning Sign | Why It Is a Problem |
| Pop-ups that will not close | Often lead to ads or scams |
| Forced redirects | Send you to unrelated or harmful pages |
| Several fake “Download” buttons | Hide the real link among traps |
| No owner or contact details | No one is accountable |
| Pressure to act fast | Designed to stop you from thinking |
Does HTTPS Mean a Website Is Safe?
No, it does not. HTTPS only means the link between your browser and the site is encrypted. It does not prove the site has good intentions. Scam pages can get HTTPS certificates easily. The padlock tells you that nobody can snoop on the connection. It does not tell you the owner is honest. Treat the padlock as one small clue and never as a safety stamp.
Can You Trust Online Reviews and Security Claims?
Not blindly. Fake reviews are cheap to produce. Some sites even paste “100% safe” or “virus-free” badges that nobody checked. A badge that the site gives itself is a claim and not proof. Look for reviews on independent platforms and read the negative ones first. Also compare several sources. If every positive review uses the same words, be suspicious.
How to Verify Claims About AIO-TLP371
Use a short, repeatable method. First, find the original source of the claim. Second, look for independent confirmation from a researcher, regulator, or named company. Third, check the date, because old stories often get new labels. Fourth, ask whether a real victim is named. This data leak source verification takes minutes. It also protects you from sharing verified versus unverified claims as if they were the same thing.
What Are the Risks of TheJavaSea.me Leak Downloads?
Here is the irony. People who hunt for leaked data may end up leaking their own. Any AIO-TLP371 file you find could hide harm. The AIO-TLP371 security risks exist whether the leak is real or fake. A fake archive can carry a virus. A real one can carry stolen private data. Either way, you gain nothing and risk a lot.
These data exposure risks reach beyond your device. Your accounts, your money, and your identity can suffer. The table below sums up the main threats. Each one is explained in the sections that follow.
| Risk | How It Happens | Possible Impact |
| Malware | Hidden in files or archives | Device takeover, data loss |
| Phishing | Fake pages and buttons | Stolen logins or payments |
| Password theft | Info-stealing programs | Account takeover |
| Privacy harm | Handling leaked personal data | Harm to real people |
| Tracking | Cookies, permissions, add-ons | Unwanted spying and spam |
| Legal trouble | Unauthorized copies | Fines or other penalties |
Malware Hidden in Downloaded Files
Archives can hide bad code. Malware hidden in downloads often looks harmless. It may sit inside a script, a shortcut file, or a document with macros. Attackers rely on curiosity to make you open it. These malware risks are higher with suspicious archive files from unknown sites. Even a single click can install spyware or ransomware. Therefore, the safest plan is to never open suspicious file downloads at all.
See Also: Trwho.com Review: Technology Features, Security, Privacy, and Online Safety
Phishing Pages, Fake Download Buttons, and Redirects
Many “download” pages are traps. Phishing download pages copy real sites and ask you to log in. Others offer surveys, prizes, or paid access that never arrives. Fake buttons send you to ads or harmful software. Because of this, one wrong click can cost you money or data. Strong phishing and malware prevention starts with closing the page the moment it feels off.
Password Theft and Account Compromise
Some malware steals saved logins. It reads your browser and sends passwords to an attacker. This puts browser credential security at risk. Then password reuse risks make things worse, because one stolen password can open many doors. A single mistake can lead to compromised online accounts. Good credential theft prevention means unique passwords and a trusted password manager.
Privacy Risks and Exposure of Leaked Data
Real people sit behind leaked records. Their names, emails, and private details may be inside. Handling such files adds to their harm. This is a real personal information exposure problem and not a game. Sharing the files also spreads unauthorized data distribution. Even if you only look, you may store sensitive data on your device. That creates leaked database concerns for you as well.
Browser Tracking and Unwanted Permissions
Risky sites often push trackers. They ask to send notifications. They may suggest a browser add-on. Each approval gives them more access. Notification spam can lead to more scam links. Some add-ons read everything you type. For better online privacy protection, deny unneeded permissions and review your installed extensions often.
Legal and Copyright Concerns
Downloading or sharing unauthorized material may break the law. Rules differ by country, so what is allowed in one place may be banned in another. Leaked company files can involve copyright and data privacy compliance rules. Personal data can raise even stricter duties. This is not legal advice. If you are unsure, skip the download and ask a qualified professional.
How to Check Whether Your Information Has Been Exposed
You never need the leak file itself. That is the good news. Safe tools can tell you if your email or password appeared in a known breach. Using them is faster and far safer than searching shady sites. This is smart data security practices in action.
Still, no tool sees everything. Some leaks never reach public databases. So use more than one layer. Combine breach checks, strong passwords, and account alerts. This layered approach supports online security best practices and keeps working even when one check misses something.
Use Reputable Data Breach Notification Services
Start with data breach notification services. Have I Been Pwned lets you enter an email and see known breaches. It also offers alerts for future exposures. Many password managers and browsers include similar breach monitoring services. These data breach monitoring tools show exposed email addresses without risky downloads. A clean result is good news but not a guarantee.
Check Official Security Advisories
Next, look at trusted notices. Companies post alerts when they confirm an incident. Government agencies such as CISA share official cybersecurity advisories. Your national cyber agency may do the same. These sources rely on checked facts. Because of that, they carry far more weight than a random blog post about a leak label.
Avoid Downloading Unknown Leak Archives
Here is the short recap. Unknown archives can hold malware. They can lead to phishing. They can expose private data. They can also cause legal trouble. And they rarely tell you more than a breach checker would. Unknown archive downloads give you risk without reward. Skip them.
What to Do If You Downloaded a Suspicious AIO-TLP371 File
Don’t panic. But do act today. Quick steps limit the damage. Good cybersecurity incident response at home follows four simple moves. Stop using the file. Scan your device. Change your passwords. Then watch your accounts.
Speed matters because stolen logins are often used within hours. Start from the first step and work down. If you ran the file, disconnect from the internet right away. Use a different, clean device for password changes. This keeps new passwords away from any spying program.
Stop Opening or Sharing the File
Leave the file alone. Do not open it again. Do not forward it to friends or colleagues. If you already ran it, unplug from Wi-Fi or the network cable. This can stop malware from sending data out. Move the file to a safe spot only if your security software tells you to. Otherwise, wait for the scan.
Scan Your Device With Reputable Security Software
Run a full scan with trusted antivirus software. Update its definitions first. An offline or boot-time scan can catch stubborn threats. If the scan finds trouble, follow the removal steps carefully. For severe cases, use a rescue disk or ask a professional. As a last resort, back up clean personal files and reinstall the system.
Change Exposed Passwords and Enable Multifactor Authentication
Use a clean device for this step. Change email and banking passwords first. Email matters most because it can reset other accounts. Make each password unique. Next, turn on multi-factor authentication. An app or security key works better than text codes. Strong password security plus MFA gives real leaked credentials protection. These steps also help with identity theft prevention.
Check Your Accounts and Browser for Suspicious Activity
Now look for signs of trouble. Check recent logins on email and social accounts. Review forwarding rules, since attackers often add hidden ones. Remove browser extensions you do not know. Delete saved cards you do not trust. Watch your bank statements for odd charges. Careful checks support account compromise prevention and catch problems early.
See Also: 20xBusiness.com Review: Features, Credibility, Ownership, and Safety
TheJavaSea.me Down: How to Check Website Availability
You type the address and nothing loads. It feels odd, but it happens often. Many people search “TheJavaSea.me down” and assume something dramatic occurred. In truth, most outages have dull causes. A server may be busy. A domain may have lapsed. A host may have removed the page.
Downtime tells you nothing about trust. A site can be offline and still be risky when it returns. A site can be online and still be harmful. So never treat an outage as proof of a takedown or a hack. Focus on safe checks instead.
Common Reasons a Website May Be Unavailable
Several simple things can break access. Servers crash or go into maintenance. Domain names expire. Hosting companies suspend accounts. Internet providers or governments may block certain sites in some regions. A cyberattack can also knock a site offline. Each cause looks the same from your screen, so you cannot guess from the error alone.
How to Check Website Status Safely
Use a reputable website status checker. It tests the site from outside your network. You can also try a different network or device. If the checker says the site is up but you cannot reach it, a local block may exist. Never log in on a page that only looks like the site. Never enter passwords while testing availability.
Why Unverified Mirror Websites Can Be Risky
When a site goes down, mirror sites often pop up. They claim to be the same service. Yet anyone can copy a name. A mirror may serve malware or run a phishing page. This weakens online archive security and digital archive safety. You cannot tell who runs it. If you cannot confirm a mirror’s owner, do not visit it.
TheJavaSea.me Alternatives: Safer and Legal Options
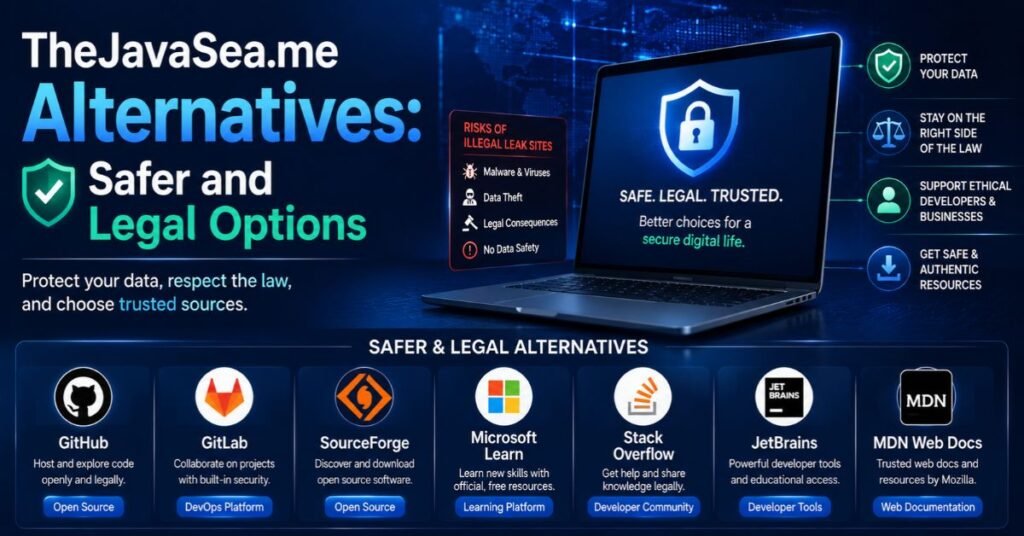
Looking for files? You have better doors to knock on. Legal sources protect your device and your record. They also support the people who made the work. Better yet, they give you clean files with clear licenses. That is a win for digital information safety.
Safer choices also save time. You skip pop-ups, scans, and worry. Pick the option that fits your need. The sections below cover software, code, learning material, security news, and direct requests to the owner.
Official Software Websites and Authorized Marketplaces
Go straight to the maker. Official sites and verified app stores offer signed, tested downloads. Check the web address carefully before you click. Look for publisher names and update histories. Many vendors also offer free trials or free tiers. These routes cut malware risks sharply.
Trusted Open-Source Repositories
Open-source code lives on well-known hosting platforms. Pick projects with active updates and many contributors. Read the license first. Verify checksums or signed releases when offered. This helps confirm the file is the one the author released. Strong data security practices include checking before you run.
Free and Open Educational Resources
You can learn a lot without risky sites. Open courseware, public-domain libraries, and Creative Commons material are free and legal. Universities and libraries host many of them. You get quality content and peace of mind. It is a far better path than hunting through a leaked data collection.
Official Cybersecurity Advisories and Breach Notifications
If you want real breach news, use real sources. National response teams, regulators, and company notices share confirmed facts. They explain what happened and what to do. This is the best place to follow security research findings. It also keeps you away from suspicious download websites.
Contacting the Original Publisher or Data Owner
Sometimes the best move is to ask. Write to the publisher for a licensed copy. If you think private data is exposed, tell the data owner. This supports responsible cybersecurity reporting. It also helps fix the problem at its source. Most organizations have a security contact page.
How to Evaluate Articles About TheJavaSea.me Leaks AIO-TLP371
Not every article that sounds sure is sure. Confident writing is easy. Proof is hard. Many pages about this topic mix real facts with guesses. A sharp reader can tell them apart. Build a few habits and you will spot weak claims fast.
Search volume is not evidence either. A term can top the charts and still have no proof behind it. Strong cybersecurity awareness means asking how a writer knows what they say. Good reporting shows its sources and admits what is unknown.
Separate Verified Facts From Speculation
Sort each claim into a bucket. Verified claims have clear sources. Unverified claims lack them. False claims clash with known facts. The table below shows how this works for our topic.
| Statement | Bucket |
| The search phrase exists | Verified |
| AIO often means All-In-One | Reasonable but not confirmed for this file |
| It is a confirmed breach | Unverified |
| TLP371 is an official FIRST label | False |
Check Sources, Publication Dates, and Evidence
Trace each claim to its first source. Does the article link to a regulator, a researcher, or a company? Or does it link to another blog? Also check dates. Old leaks often get recycled under new names. This is a core part of leaked data authenticity checks. A good online archive investigation always starts with the original post.
Be Cautious of Unsupported Technical Claims
Watch for details that seem too perfect. An exact record count with no source is a red flag. So are claims about AI features, attack methods, or encryption with no proof. Remember that no reliable evidence supports any of these for AIO-TLP371. Proper technical identifier verification needs real data. Without it, such claims are fiction.
See Also: BD268XZ Explained: Meaning, Uses, Applications, and What to Know
What Businesses Should Do About Unverified Leak Claims
Overreacting costs money. Ignoring a real breach costs more. Businesses must find the middle path. When a leak label mentions your brand, stay calm and gather facts. A strange name in a search result is a reason to investigate. It is not proof of compromise.
Start with a plan that is already written. Teams with tested incident response procedures move faster and make fewer mistakes. They also avoid sharing guesses with the public. The sections below show a sensible order of action.
Investigate Potential Data Exposure Responsibly
Begin with your own evidence. Review authentication logs and unusual access patterns. Check endpoint alerts and cloud activity. Look for staff credentials in known breach sources. Run cybersecurity forensic analysis if signs look real. Preserve logs so experts can study them later. Do not download the leak archive yourself, since that adds risk and may raise legal issues.
Protect Affected Users’ Privacy
Put people first. If risk looks real, force password resets for affected accounts. Limit internal access to any sensitive records. Avoid copying or storing leaked material. This supports personal data protection and data privacy compliance. It also shows customers that you take their trust seriously.
Communicate Security Findings Transparently
Share facts and only facts. Say what you know and what you do not. Avoid guessing about causes or numbers. Follow local notification laws and deadlines. Clear updates build trust. Vague or false statements do the opposite. Calm, honest messaging is the mark of a mature security team.
Frequently Asked Questions
What Is TheJavaSea.me Leaks AIO-TLP371?
TheJavaSea.me leaks AIO-TLP371 is a search phrase linked to an alleged online archive. Its contents, origin, size, and authenticity are not independently confirmed. Treat it as an unverified leak archive until trusted researchers or affected organizations publish real evidence.
Is AIO-TLP371 a Confirmed Data Breach?
No. There is no public proof of a known victim, a verified record count, or an official notice. The label may point to old, recycled, or misdescribed material. Until real data breach evidence verification appears, avoid calling it a confirmed breach.
Is TheJavaSea.me Safe to Visit?
Treat it with caution. Little reliable information exists about the site’s owners or practices. Sites like this often use pop-ups, redirects, and fake buttons. If you must research the topic, rely on trusted news and security sources instead of visiting the site.
Does TLP371 Belong to the Official Traffic Light Protocol?
No. FIRST’s TLP 2.0 includes only TLP:RED, TLP:AMBER+STRICT, TLP:AMBER, TLP:GREEN, and TLP:CLEAR. TLP371 is not a valid label. The name may only borrow the look of a real security term to seem official.
Can AIO-TLP371 Downloads Contain Malware?
Yes, that is possible. Any unknown archive can hide scripts, shortcuts, or booby-trapped documents. Fake download pages can also install harmful software. You cannot see these threats by looking at a file name, so the safest choice is not to download it.
Should I Download AIO-TLP371 to Check My Information?
No. You do not need the file. Safer tools like Have I Been Pwned can show if your email appeared in known breaches. Downloading unknown archives adds malware risks, scam risks, and possible legal problems without giving you reliable answers.
What Should I Do If My Data Has Been Exposed?
Change your passwords, starting with email and banking. Use a different password for every account. Turn on multi-factor authentication. Review recent logins and watch your statements. If money or identity data is involved, contact your bank or the official service directly.
What Are the Safest Alternatives to TheJavaSea.me?
Use official software sites, verified app stores, trusted open-source repositories, and open educational resources. For breach news, follow official advisories and breach notification services. If you need a specific file, ask the original publisher for a licensed copy.
Conclusion
Here is the short version. TheJavaSea.me leaks AIO-TLP371 is a real search term. The evidence behind it is thin. TLP371 is not an official TLP label. And downloading unknown archives carries real cybersecurity risks. The most honest description is an unverified leak archive wrapped in uncertainty.
So what should you do next? Use trusted breach checkers. Turn on multi-factor authentication. Keep passwords unique. Skip risky downloads. Then share this guide with someone who is curious about the label. A little cybersecurity awareness protects you far better than any leaked file ever could.